
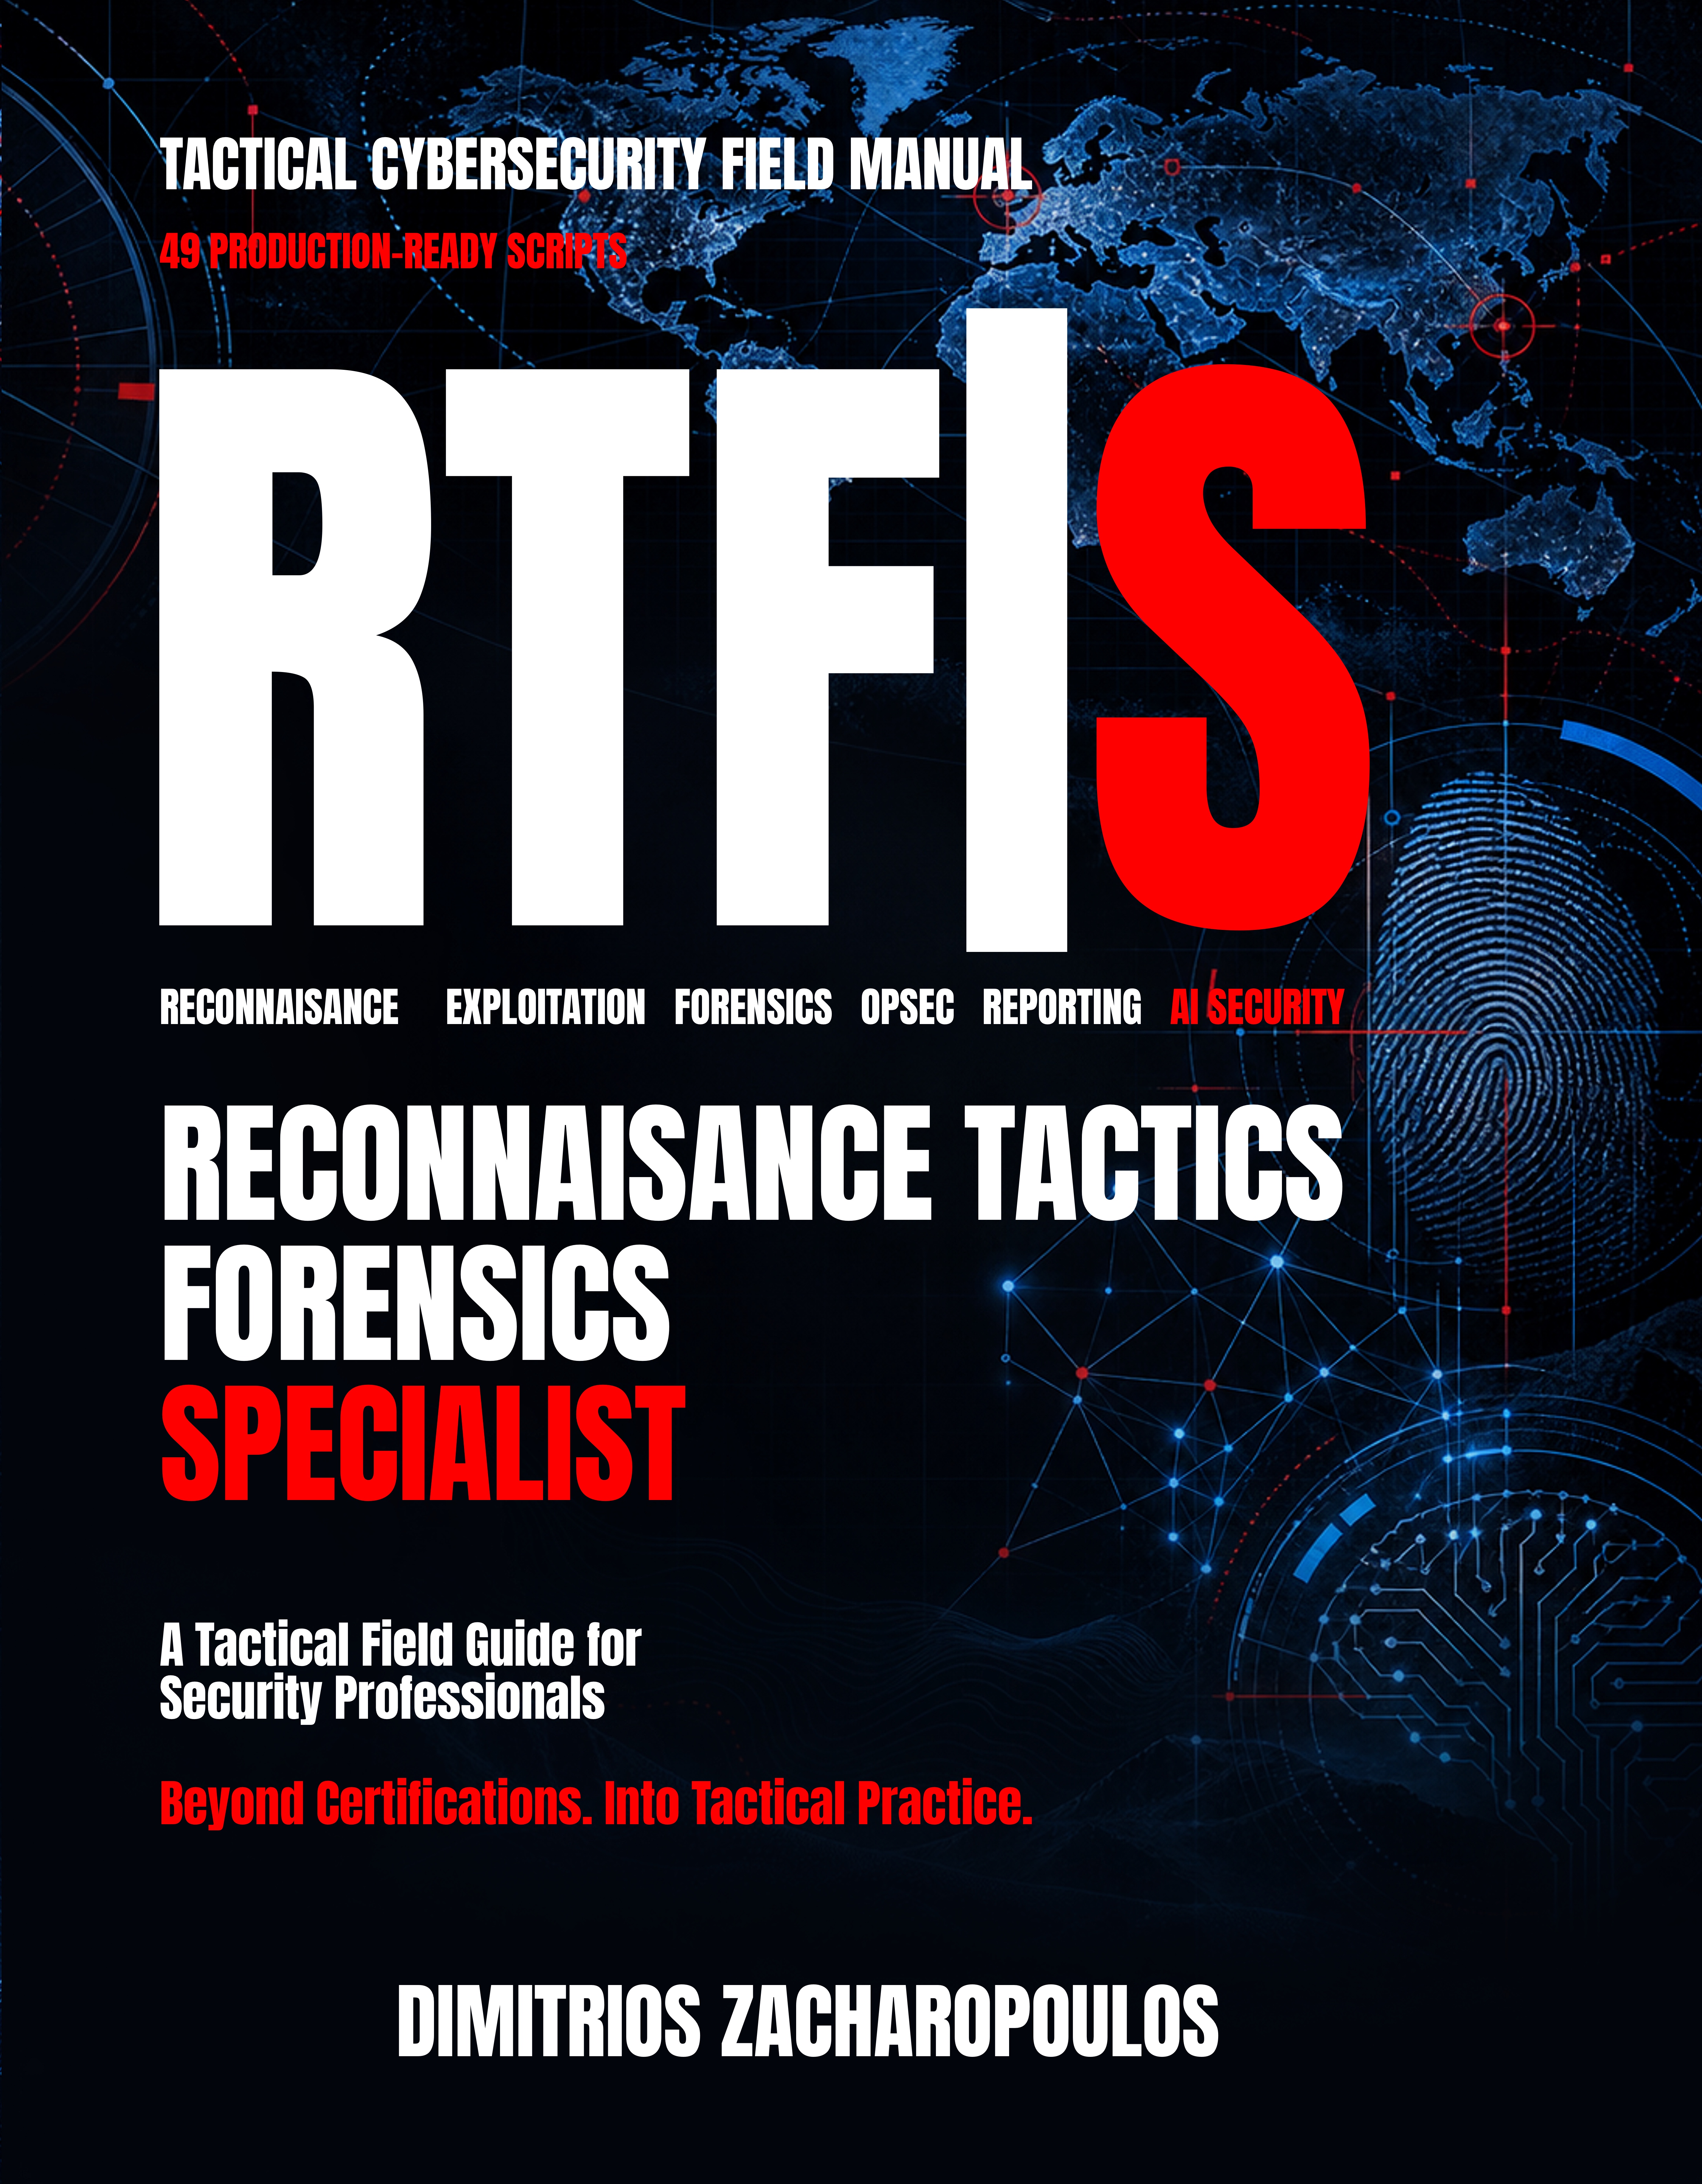
THE OFFICIAL RTF|S FIELD GUIDE
RTF|SReconnaissance Tactics Forensics Specialist
A Tactical Field Guide for Security Professionals
- Pages
- 410
- Chapters
- 18
- Parts
- 5
- Scripts
- 49
Beyond certifications. Into tactical practice.
Certifications prove knowledge.
Fieldwork builds capability.
AI now changes both.
RTF|S is the official technical field guide for security professionals who have passed the certifications and now want to become world-class operators. It is 410 pages of commands, tools, scripts, workflows, and field methods that take you from exam readiness to operational confidence.
Written by a cybersecurity and digital forensics specialist with over 40 years of real engagement experience, this book covers the full practitioner lifecycle across five integrated domains: reconnaissance, tactics, forensics, operational security, and reporting.
Every technique is explained at depth. Every tool is shown the way operators actually use it. And with 49 production-ready scripts in Python, Bash, and PowerShell, you are building capability as you read.
The practitioner lifecycle
Five domains. One operational mindset.
From mapping a target to explaining the business impact, the disciplines connect into a repeatable field workflow.
Reconnaissance
Map the target with practical reconnaissance, enumeration, and service-discovery workflows. Work with real Nmap and NSE syntax across SMB, Active Directory, Linux, web, database, and cloud assessments.
Tactics & exploitation
Turn findings into informed action through exploitation and post-exploitation workflows, including privilege escalation and credential attacks.
Digital forensics
Reconstruct what happened with memory analysis, disk and file-system forensics, log analysis, and network forensics.
Operational security
Understand operational visibility, operational security, and artifact cleanup across Windows and Linux.
Reporting & business impact
Turn technical findings into useful outcomes with reporting templates, field notes, analyst tips, and repeatable procedures.
The curriculum
Inside RTF|S: the complete table of contents.
Follow the progression from a specialist mindset and your own lab environment through reconnaissance, exploitation, digital forensics, operational security, reporting, AI security testing, and a custom toolkit.
- Legal and Ethical Use
- Foreward
- Preface: The Gap Nobody Talks About
- Chapter 1Thinking Like a Specialist
- Chapter 2Building Your Lab Environment
- Chapter 3Passive Reconnaissance
- Chapter 4Active Reconnaissance
- Chapter 5Web Application Reconnaissance
- Chapter 6SMB and Windows Service Enumeration
- Chapter 7Active Directory Enumeration
- Chapter 8Linux and Service Enumeration
- Chapter 9Exploitation and Why Most Exploits Fail
- Chapter 10Exploitation in Practice
- Chapter 11Post Exploitation
- Chapter 12Digital Forensics: Foundations and Memory Analysis
- Chapter 13Disk and File System Forensics
- Chapter 14Log Analysis and Network Forensics
- Chapter 15Operational Security
- Chapter 16Reporting That Earns Respect
- Chapter 17AI in Security Testing: Using It and Breaking It
- Chapter 18Building the RTF|S Custom Toolkit
AI in the field
Use AI. Understand its attack surface.
Bring AI into security workflows, then examine the weaknesses of modern AI systems themselves.
- AI-assisted security workflows using ChatGPT, Claude, Ollama, and LLaMA.
- Modern AI system testing: prompt injection, data leakage, MCP security, and agent abuse.
- Adversarial testing with Garak, PyRIT, PromptBench, and the OWASP Top 10 for LLM Applications.
- ChatGPT
- Claude
- Ollama
- LLaMA
- Garak
- PyRIT
- PromptBench
Build your capability
49 scripts. Your own toolkit.
Production-ready scripts in Python, Bash, and PowerShell, with guidance on building your own custom toolkit so you never depend entirely on commercial tools.
- Python
- Bash
- PowerShell
Put it into practice
Hands-on. Field-ready.
Hands-on labs, real-world examples drawn from decades of consulting, testing, and investigation, and repeatable procedures you can return to in the field.
Companion resources
Keep building beyond the page.
Companion labs, scripts, and resources are available at OBISEC.COM.
Explore the companion resources on the Obisec website.
Visit ObisecWho this book is for
For professionals ready to go deeper.
Penetration testers, red teamers, forensics investigators, and security engineers moving beyond CEH, CHFI, ECIH, CPENT, CISSP, CISA, CISM, and OSCP.
If you are comfortable at the command line and want the depth that separates practitioners from specialists, this book was written for you.
- CEH
- CHFI
- ECIH
- CPENT
- CISSP
- CISA
- CISM
- OSCP
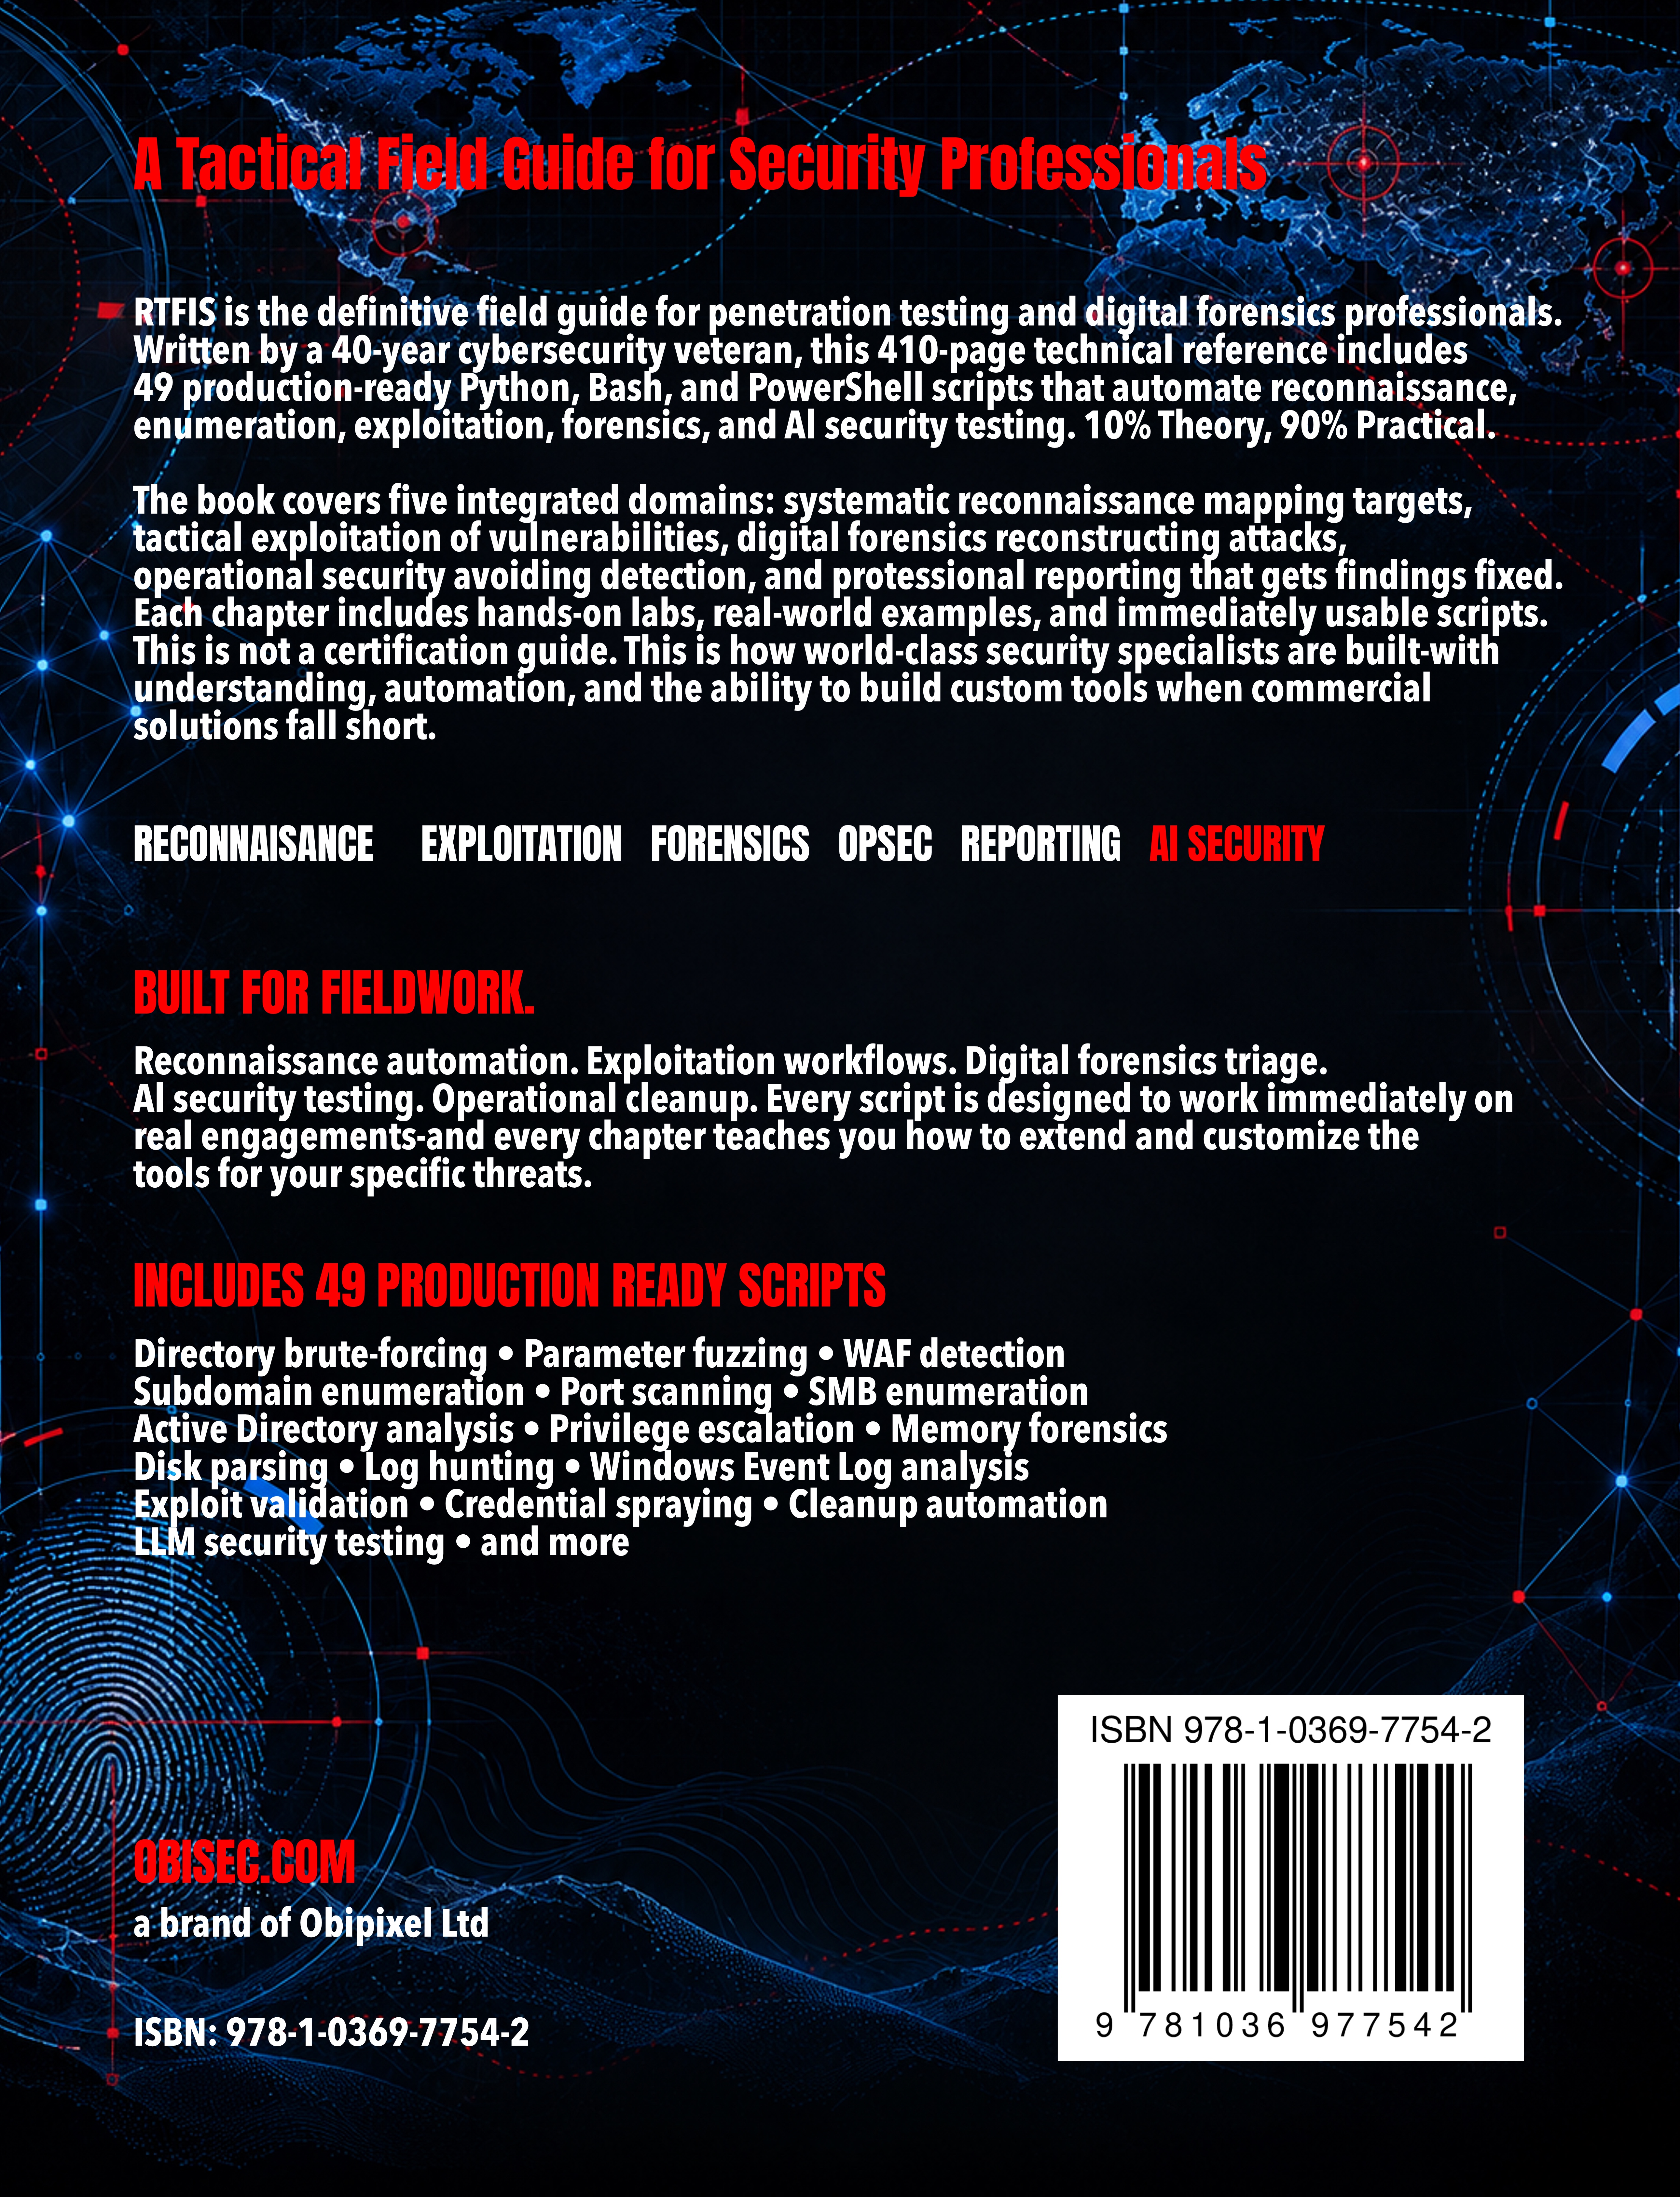
Cover art
The field guide, front to back.
About the author
Dimitrios Zacharopoulos
An accomplished fiction writer and a cybersecurity and digital forensics specialist, Dimitrios brings 40 years in IT and 36 years in cybersecurity to this field guide.
He holds CISSP, OSCP, CEH, ECIH, EDRP, CHFI, CPP, CAIMLP, CAAINE, AMBSIF, GPTPv2 and CBCP among numerous certifications, and has spent decades delivering security consulting, penetration testing, forensic investigation, and advanced technical training to professionals across government, finance, defence, telecoms, law enforcement, and enterprise.
RTF|S distils that experience into a single, field-ready reference.
Book details
Your field reference.
- Title
- Reconnaissance Tactics Forensics Specialist (RTF|S)
- Subtitle
- A Tactical Field Guide for Security Professionals
- Author
- Dimitrios Zacharopoulos
- Category
- Non-fiction · Technical guide · Cybersecurity & digital forensics
- Structure
- 18 chapters across 5 parts
- Length
- 410 pages
- Scripts
- 49 production-ready scripts · Python, Bash & PowerShell
- Resources
- Companion labs, scripts, and resources at OBISEC.COM
- Available at
- Obisec Direct & Amazon · Apple Books coming soon
Take the next step
Beyond certifications.
Into tactical practice.
Make RTF|S part of your professional toolkit.